CMMC compliance on Microsoft 365 starts with the right environment. See what NIST 800-171 Level 2 requires and how to configure your tenant for assessment.

 CMMC Compliance on Microsoft 365: What a Level 2 Assessment Actually Requires
CMMC compliance on Microsoft 365 starts with the right environment. See what NIST 800-171 Level 2 requires and how to configure your tenant for assessment.
 Protecting Company Data on BYOD Devices with Intune
Learn how to protect company data on BYOD devices with Microsoft Intune, using app protection policies, Conditional Access, MAM, and selective wipe.
 How to Block Unsafe Websites on Work Devices
Protect work devices from phishing, malware, and risky web content by using Microsoft Defender and Intune to block unsafe websites across your organization.
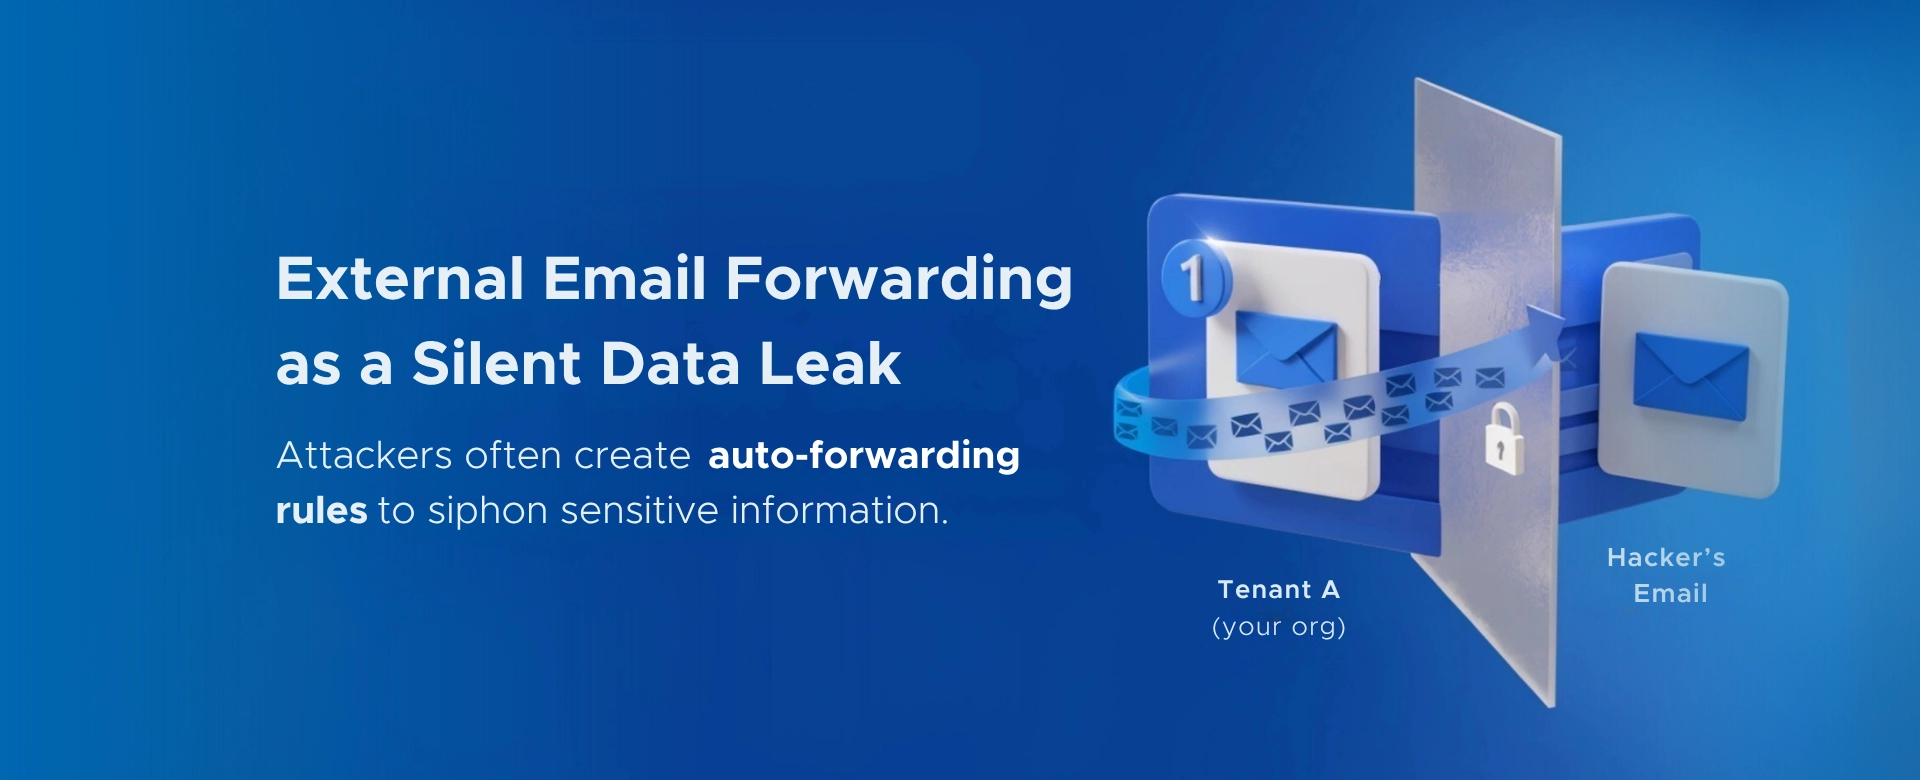 Your Microsoft 365 Tenant Has a Silent Data Leak. It Requires No Malware.
Your Microsoft 365 tenant can leak data silently - no malware, no alerts. Learn how simple misconfigurations enable ongoing email and data exfiltration.
 Security Alerts That Nobody Investigates - And Why That’s More Dangerous Than Having None
Security alerts mean nothing if no one investigates them. Ignored alerts create false confidence - and give attackers the time they need to cause real damage.
 The Silent M365 Risk Most CXOs Discover Too Late: External Access That Never Expired
A hidden Microsoft 365 risk many CXOs overlook - expired external access that quietly breaks Zero Trust and exposes organizations to serious security gaps.
 The Shadow Admin Problem in Microsoft 365 – A Silent Risk Most CXOs Miss
Shadow admins in Microsoft 365 create invisible security, compliance, and governance risks - often without CXOs realizing how exposed their environment truly is.
 Your Defender Is On. So Why Is CEO Impersonation Still Working?
Defender being “on” isn’t enough. Why CEO impersonation still works in Microsoft 365 - and how misconfigured trust exposes organizations to fraud.
 The Most Dangerous Permission in SharePoint Is Hiding in Plain Sight
A hidden SharePoint permission - “Everyone Except External Users” - quietly breaks Zero Trust, exposing internal data and amplifying risk in the age of Copilot.
 Your Shared Mailbox Is Quietly Breaking Zero Trust - And Most Organizations Don’t See It
Shared mailboxes often bypass Zero Trust controls - creating silent security gaps. Here’s how excessive access quietly puts organizations at risk.