Learn how to protect company data on BYOD devices with Microsoft Intune, using app protection policies, Conditional Access, MAM, and selective wipe.

I have helped organizations secure their Microsoft 365 tenant for years, including contractors in the defense supply chain. Firewalls were solid. MFA was enabled.
Their Microsoft 365 looked clean. Yet the Controlled Unclassified Information they were paid to protect sat in a commercial tenant that would never qualify for the assessment they were about to fail.
Here is the uncomfortable truth about CMMC compliance. The exotic control rarely sinks a defense contractor. The environment your data lives in and the permissions no one audited usually do.
What compliance demands on the Microsoft stack is simpler, and harder, than a product.
If your organization handles Controlled Unclassified Information and a CMMC requirement is heading for your next contract, the environment and configuration decisions are easier to fix now than under an assessment deadline. A short, consultative conversation with a Microsoft MVP-led team is usually worth having before scope is locked.
CMMC stands for Cybersecurity Maturity Model Certification, the Department of Defense program that verifies contractors and subcontractors are protecting sensitive federal data to a defined standard. The current model, CMMC 2.0, was codified in the Department of Defense program final rule that took effect on December 16, 2024.
The model has three levels, and the difference between them is the data you handle.
One point trips up almost every early conversation I have, so let me be precise. NIST published Revision 3 of SP 800-171 in May 2024. The CMMC program rule, however, ties Level 2 to the 110 requirements of NIST SP 800-171 Revision 2.
The transition to Revision 3 is a separate regulatory process still working through rulemaking, so the safe move is to confirm the exact revision named in your specific contract and build to that. Do not assume the newest publication is the one you will be assessed against.
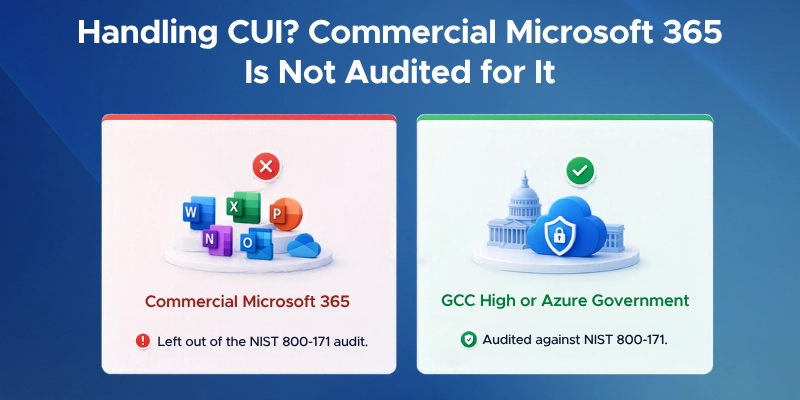
Here is the belief I most want to interrupt, because it feels reasonable and it is wrong for CUI. Microsoft 365 is a strong foundation for CMMC, and the platform provides the controls. Your current tenant being the right container for regulated data is the part that does not follow.
Three points decide it:
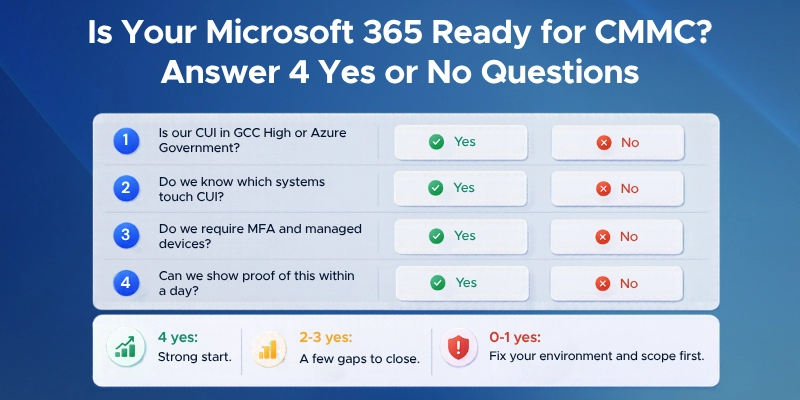
On paper, "we have Microsoft 365" sounds like a head start. In reality, the environment question comes first.
Get the framing right before the configuration work, because getting it wrong is how organizations overspend and still fail. No tool delivers compliance. A C3PAO assesses your organization, your configuration, and your documentation, so certification is an outcome of how you run the environment rather than a box you buy.
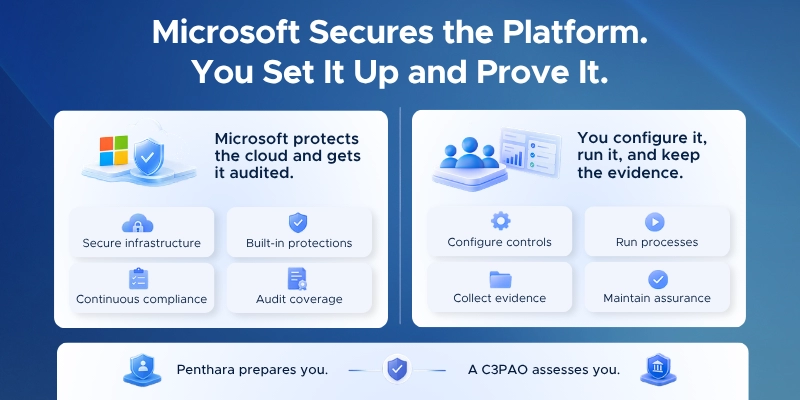
Microsoft is explicit about the split:
You do not have a compliant tenant because you bought the right licenses. You have one because you configured, governed, and evidenced it. A license is not a control.
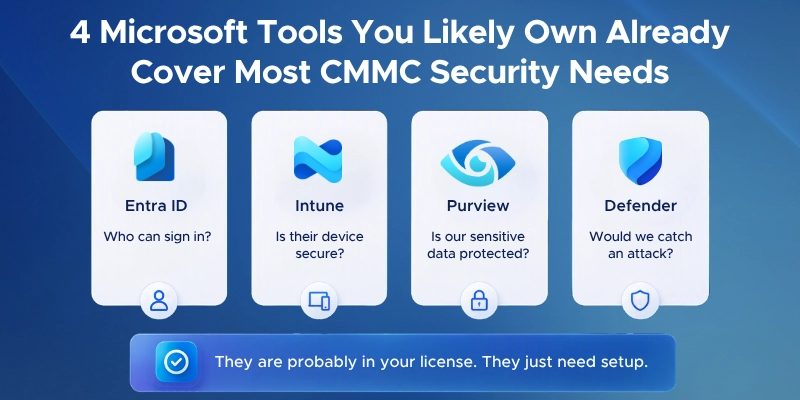
Once you are in the correct environment, the 110 requirements of NIST SP 800-171 map to capabilities you largely already have in Microsoft 365 and Azure. The work is configuration and evidence rather than a shopping list of third-party bolt-ons. Here is the ladder I walk contractors through.
Decide where CUI will live and draw the boundary. For most CUI workloads, that means Microsoft 365 GCC High or Azure Government environments that Microsoft attests against NIST SP 800-171. Define your assessment scope narrowly and deliberately: the fewer systems that touch CUI, the smaller and cleaner your assessment.
That scoping choice governs cost, so make it consciously.
For your admin: GCC High is not self-service. Microsoft limits it to organizations with qualifying data such as CUI or ITAR, validates your eligibility through a request form before provisioning, and sells the licenses only through authorized government partners. Build that lead time into the plan.
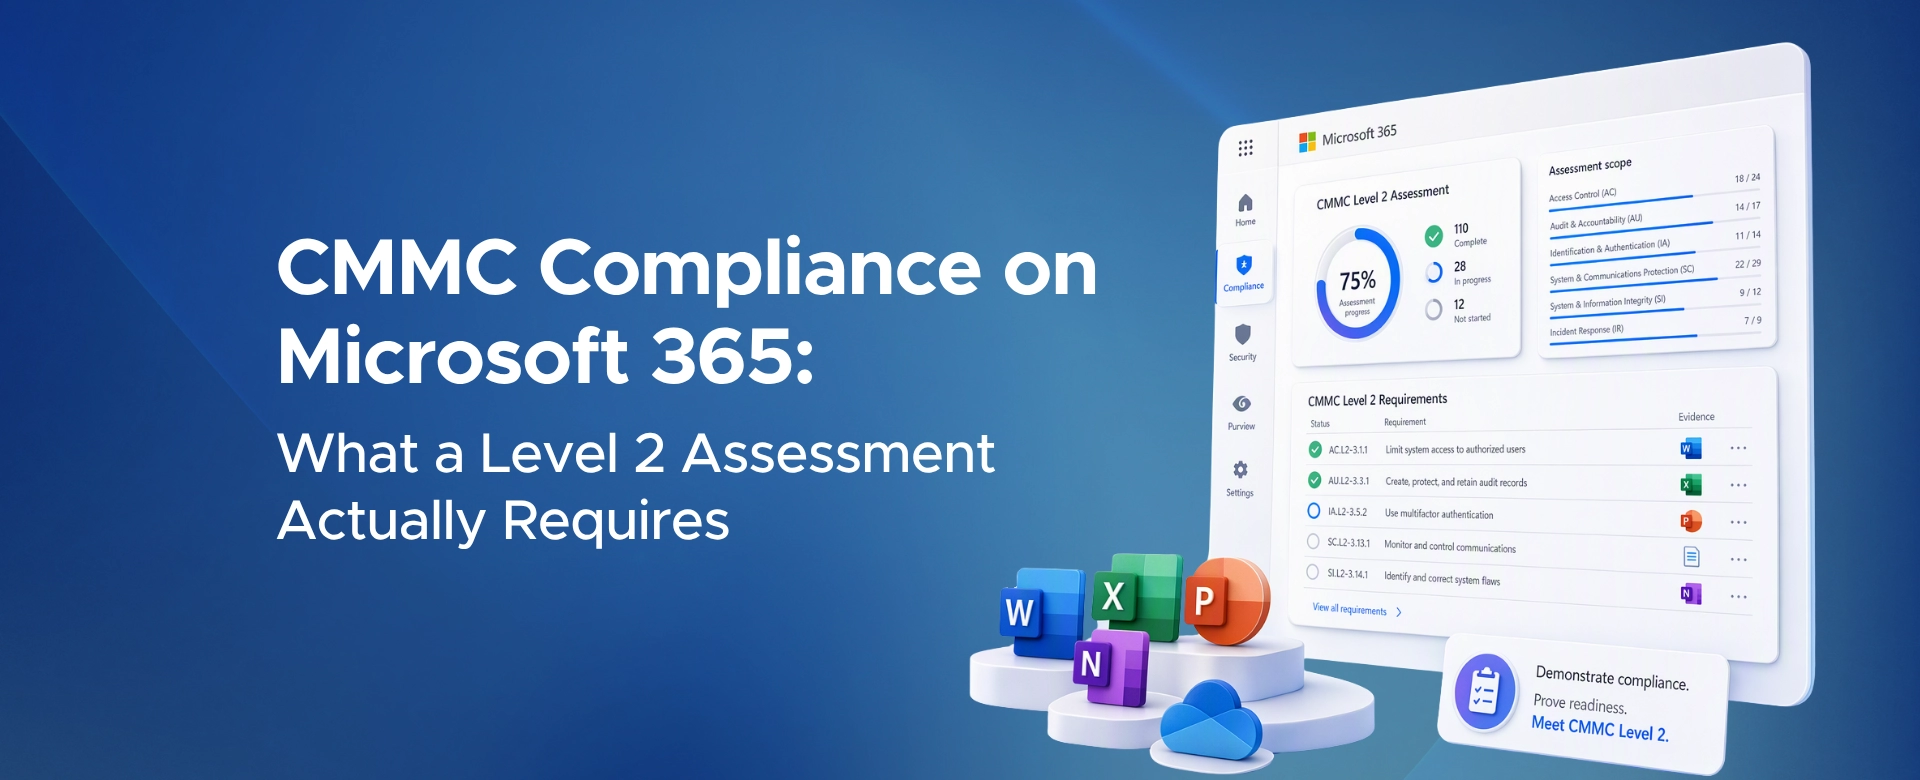
Microsoft Purview Compliance Manager offers a premium assessment template built for NIST SP 800-171, which underpins CMMC Level 2. The template tracks the requirements, assigns improvement actions, and stores the evidence an assessor will ask for. Compliance without documentation does not pass, and this is where the documentation lives.
For your admin: add the assessment in the Microsoft Purview portal under Compliance Manager, then Assessments, then Add assessment, and choose the NIST SP 800-171 template that underpins Level 2. Each requirement carries improvement actions and an evidence store, which becomes the backbone of your System Security Plan (SSP) and Plan of Action and Milestones (POAM).
Access Control and Identification and Authentication are two of the largest NIST SP 800-171 families. Enforce phishing-resistant multi-factor authentication and least privilege with Conditional Access in Microsoft Entra ID, and make privileged roles just-in-time and time-bound with Microsoft Entra Privileged Identity Management (PIM) so that standing Global Administrator access, the permission attackers want most, is eliminated by design.
CUI reached from an unmanaged laptop is CUI you cannot defend. Use Microsoft Intune to require compliant, encrypted, and configured devices before they touch regulated data, which supports the Configuration Management and Media Protection requirements with enforceable policy rather than a written promise.
Label CUI and enforce handling with Microsoft Purview Information Protection sensitivity labels and Microsoft Purview Data Loss Prevention (DLP), so that protection follows the file and unauthorized sharing is blocked rather than discovered after the fact.
Audit and Accountability, Incident Response, and System and Information Integrity require that you can see and respond to an event. Microsoft Defender XDR and Microsoft Sentinel provide the logging, detection, and incident response evidence an assessor expects, and turn "we would probably notice" into a record you can show.
No third-party security suite is required to satisfy the core of this. For most contractors, the tools are already present. The gap is that they are unconfigured.
To make that concrete, here is how the largest NIST SP 800-171 families line up with the Microsoft control and where you configure it.
| NIST SP 800-171 family | Microsoft control to configure | Where you configure it |
|---|---|---|
| Access Control (AC) | Conditional Access policies that require a compliant device and phishing-resistant MFA | Microsoft Entra admin center, under Protection then Conditional Access |
| Identification and Authentication (IA) | Phishing-resistant methods such as FIDO2 and Windows Hello for Business, plus just-in-time roles with PIM | Microsoft Entra admin center, Authentication methods and Privileged Identity Management |
| Audit and Accountability (AU) | Audit logging with extended retention, plus long-term log retention for investigations | Microsoft Purview portal (Audit) and Microsoft Sentinel |
| Configuration Management and Media Protection (CM and MP) | Device compliance and configuration baselines with disk encryption enforced | Microsoft Intune admin center, under Devices |
| System and Communications Protection (SC) | Sensitivity labels and Data Loss Prevention applied to CUI | Microsoft Purview portal, Information Protection and Data Loss Prevention |
Before you scope a full CMMC program, it helps to see where your current tenant actually stands. A free Microsoft 365 security assessment gives you a grounded picture of your identity, device, and data posture, which is the same ground a Level 2 readiness effort has to stand on.
Treating CMMC as a compliance formality is tempting. The threat it exists to answer is real and documented.
The Government Accountability Office reported that the Department of Defense experienced more than 12,000 cyber incidents between 2015 and 2021, and separately found that reporting of incidents across the defense industrial base was incomplete, meaning the true figure is understated rather than overstated. Adversaries target contractors precisely because a subcontractor is often the softest path to the data a prime protects well.
Here is the logic behind CMMC. The defense supply chain is only as strong as its least-governed tenant, and for years the requirement to protect CUI existed on paper without verification. CMMC adds the verification.
If your Controlled Unclassified Information can be reached through a misconfigured permission or an unmanaged device, you do not have a compliance gap on paper. You have an exposure in production.
Readiness is very achievable on the Microsoft stack, but the sequence matters: environment, then scope, then configuration, then evidence. Getting that order wrong is what turns a manageable project into a costly one. If a CMMC requirement is heading for your contracts, it is usually worth a short conversation before an assessment deadline forces a longer one.
A few questions come up in almost every CMMC conversation with a contractor on Microsoft 365.
Does Microsoft 365 Deliver CMMC Compliance on Its Own?
No, and no product delivers CMMC compliance on its own. Microsoft provides platform controls and attests its government clouds against NIST SP 800-171, and Penthara helps you configure Microsoft 365 to support your requirements. The assessment is performed against your organization, and Level 2 certification is issued through a certified third-party assessor organization (C3PAO).
Do I Need Microsoft 365 GCC High for CMMC?
If you process Controlled Unclassified Information, then yes, in most cases. Microsoft attests that Microsoft 365 GCC High and Azure Government are aligned with NIST SP 800-171 and states that Office 365 Commercial is not in scope for that audit. The precise environment depends on your data types and contract, so confirm it against your contractual requirements before migrating.
Is CMMC Level 2 Based on NIST 800-171 Revision 2 or Revision 3?
The CMMC program rule ties Level 2 to the 110 requirements of NIST SP 800-171 Revision 2. NIST published Revision 3 in May 2024, but adopting it into CMMC is a separate rulemaking process. Confirm the revision named in your specific contract and build to that.
Who Performs a CMMC Level 2 Assessment?
For most contracts, a certified third-party assessor organization, known as a C3PAO, performs the Level 2 assessment. Some Level 2 requirements allow a self-assessment depending on the contract, and Level 3 is assessed by the government. A consultant such as Penthara helps you prepare and cannot certify you.
How Long Does CMMC Readiness Take on Microsoft 365?
Readiness time depends on your starting environment and scope. Contractors already in a government cloud with strong identity and device governance move faster than those who must migrate Controlled Unclassified Information out of a commercial tenant first. The environment and scope decisions early in the project drive the timeline more than any single control.
CMMC compliance is not won in the assessment room. The decisions you make before it are what win it: where your Controlled Unclassified Information lives, how narrowly you scope it, how tightly you govern identity and devices, and whether you can produce evidence on demand.
The good news for Microsoft-stack organizations is that the controls are largely in reach. The work is configuration, governance, and documentation, in the right order. If you are unsure your current tenant could hold CUI for a Level 2 scope, that is a short conversation worth having now.
Monthly updates, news & events from Microsoft to help your business grow.
CEO at Penthara Technologies

 Protecting Company Data on BYOD Devices with Intune
Learn how to protect company data on BYOD devices with Microsoft Intune, using app protection policies, Conditional Access, MAM, and selective wipe.
 How to Block Unsafe Websites on Work Devices
Protect work devices from phishing, malware, and risky web content by using Microsoft Defender and Intune to block unsafe websites across your organization.
 Your Microsoft 365 Tenant Has a Silent Data Leak. It Requires No Malware.
Your Microsoft 365 tenant can leak data silently - no malware, no alerts. Learn how simple misconfigurations enable ongoing email and data exfiltration.